
Secure WiFi: one passwordless SSID for everyone you trust
WPA-Enterprise on certificates. Staff on EAP-TLS with the MDM you already run, guests and residents on Passpoint and OpenRoaming, and identity deciding the VLAN. Disable an account and that person is off the WiFi everywhere.
- 99.9% RADIUS uptime SLA
- 99.999% uptime
- Regions in the UK, EU and US
- ISO 27001 and Cyber Essentials Plus
99.999% is the uptime the Purple platform runs at. 99.9% is the cloud RADIUS SLA in your contract: the floor we commit to in writing. Multi-region failover across the UK, EU and US sits behind both.
Four parts, one SSID, no passwords
Staff WiFi on EAP-TLS
Certificates delivered by Microsoft Intune, Jamf Pro, JumpCloud, Kandji, Hexnode, Iru and Addigy over SCEP, with a compliance-gated join through Conditional Access. Personal phones join through the Purple app on the same SSID.Identity-based networking
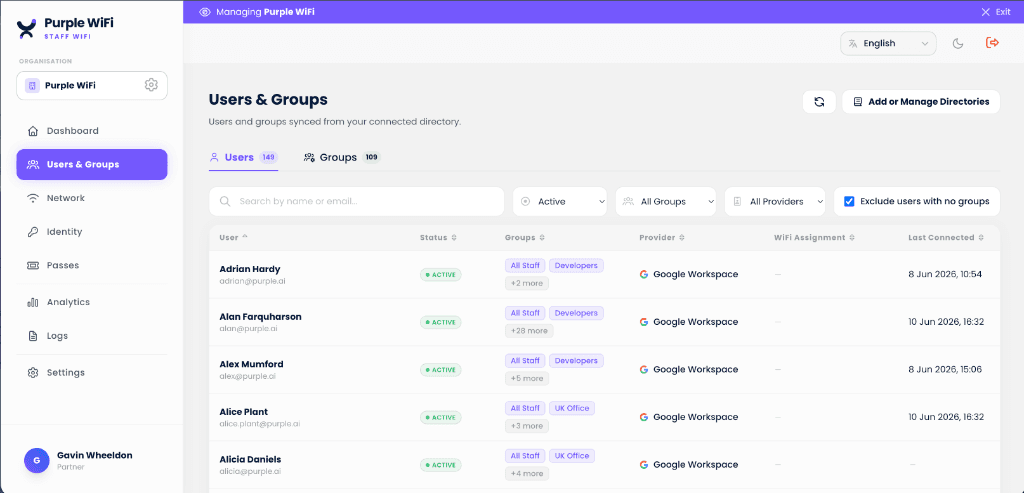
Entra ID, Okta and Google Workspace over SAML and SCIM. Group membership drives the VLAN, and leavers lose access at every site.Passpoint and OpenRoaming
A profile installs once, then connects securely at every visit with no portal. Free OpenRoaming through Connect, from a certified WBA identity broker, reaches 5 million+ hotspots.Cloud RADIUS and managed PKI
The largest cloud RADIUS in the world: 99.9% uptime SLA, multi-region failover, and certificates issued and auto-renewed for you.
How it works
Identity decides the VLAN, not the SSID
Connect your directory
Users and groups sync from Entra ID, Okta or Google Workspace over SCIM.
Issue the certificate
Purple runs the certificate authority. Your MDM delivers the certificate over SCEP, and the private key stays in the device's secure hardware.
RADIUS returns the VLAN
At authentication, cloud RADIUS checks the identity, the device's compliance and posture, and returns the VLAN and role for that person's groups.
Leavers drop off everywhere, the moment you disable them
Disable the account and access ends at every site. Live sessions are killed with RADIUS CoA.
Add-on: Purple Shield
Make this network safer and faster with Purple Shield
Purple Shield bolts onto Access or runs standalone. Set a different DNS policy per VLAN and by time of day, so staff, guests and residents each get the filtering that fits them, with dashboard analytics. Page loads up to 500% faster and 20 to 40% less web traffic. Try it free for 30 days.
FAQ
Common questions
Do staff and personal phones need separate SSIDs?
No. Managed devices get a certificate from your MDM, and personal phones go through the Purple app, both on the same secure SSID. Nobody wants a two-SSID solution. One SSID for the laptop and the phone, one report for both.
What about devices with no MDM, like student laptops and personal phones?
They sign in once in the Purple app with their work or university account, Microsoft, Google or Okta, and a WiFi pass installs on the device. Windows, macOS, Linux, iOS and Android, with no MDM.
Do we need to run a certificate authority?
No. Purple runs the certificate authority and SCEP, and certificates auto-renew.
We run ISE, ClearPass, NPS or FreeRADIUS today. What does moving involve?
Pointing your access points at Purple cloud RADIUS, the largest cloud RADIUS in the world, with 500 million logins a year. Migration is usually a weekend exercise, and we map your policies with you.
Where does eduroam fit?
Beside the three, as its own SSID. In education, eduroam makes it four. Open, secure and xPSK carry your visitors, staff, halls and devices, and eduroam keeps doing its roaming job.
Isn't PKI a project?
Not with Purple. Purple runs the certificate authority and SCEP. MDM setup takes five to ten minutes, once, and certificates auto-renew.
We already run ISE, ClearPass, NPS or FreeRADIUS. Why move?
Because you are still patching it. Purple is the largest cloud RADIUS in the world, with 500 million logins a year, a 99.9% SLA, multi-region failover and nothing for you to patch. ISE and ClearPass are appliances to buy, license and patch. NPS and FreeRADIUS are servers you run yourself. Migration is usually a weekend. We map your policies with you from your export.
Can a non-compliant device be kept off the network?
Yes. Compliance state from your MDM feeds Entra ID Conditional Access, so a device that fails a rule is refused at authentication. Device posture and MDM enrolment state are recorded in the authentication log. Supported: Microsoft Intune, Jamf Pro, JumpCloud, Kandji, Hexnode, Iru and Addigy.
Take every trusted user passwordless
Bring your directory and MDM. We map who lands on which VLAN, and you keep the plan for your estate. All in a 45-minute design session.
- Get your three-SSID plan in 45 minutesTell us what runs on your WiFi today, and a Purple network engineer maps it with you.
- Map your SSIDs onto threeOpen, secure and xPSK, on the access points you already own. You leave with the plan.
- Prove it on one site firstJudge the result on tickets and audit evidence, then roll out.
Your design session
45 minutes. Your estate. A plan you keep.
Led by a Purple network engineer. No slides. You keep the plan.