
Your directory decides who gets on, and where they land
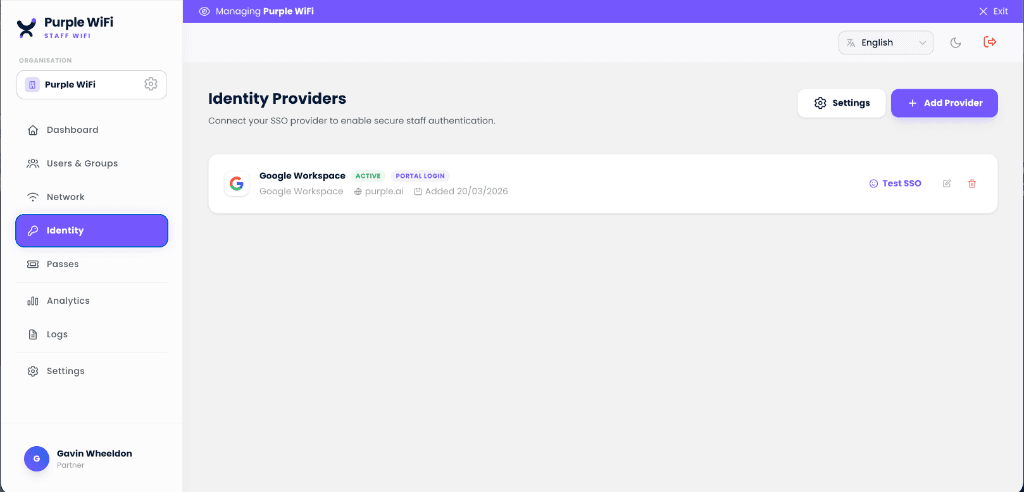
Entra ID, Okta and Google Workspace over SAML and SCIM. Group membership drives the VLAN, and Conditional Access and device posture decide who joins. Disable an account and access ends at every site, with live sessions killed by RADIUS CoA.
- SAML and SCIM
- Conditional Access honoured
- RADIUS CoA
- 99.9% RADIUS uptime SLA
Joiners, movers and leavers, handled by the directory
Joiners get the right VLAN on day one
New users and their groups sync over SCIM. Their first authentication returns the VLAN for their groups.
Movers land somewhere new without a ticket
Change a group in the directory and the next authentication returns the new VLAN.
Leavers lose access at every site
Disable the account and access ends everywhere, with live sessions killed by RADIUS CoA.
Add-on: Purple Shield
Make this network safer and faster with Purple Shield
Purple Shield bolts onto Access or runs standalone. Set a different DNS policy per VLAN and by time of day, so staff, guests and residents each get the filtering that fits them, with dashboard analytics. Page loads up to 500% faster and 20 to 40% less web traffic. Try it free for 30 days.
FAQ
Common questions
What is identity-based networking?
Every connection tied to a verified identity rather than a shared secret. A person authenticates as themselves through your directory, a device with its own certificate or key, and the network grants, scopes and withdraws access by that identity.
Which identity providers are supported?
Microsoft Entra ID, Okta and Google Workspace, over SAML and SCIM, with Entra ID Conditional Access honoured at authentication.
Does it replace our NAC?
Yes. Compliance-gated join, Conditional Access, device posture and MDM enrolment state at authentication, from Microsoft Intune, Jamf Pro, JumpCloud, Kandji, Hexnode, Iru and Addigy, with no ISE or ClearPass appliance to run.
Hand WiFi access to the directory you already trust
Bring your directory groups. We map each one to its VLAN. All in a 45-minute design session.
- Get your three-SSID plan in 45 minutesTell us what runs on your WiFi today, and a Purple network engineer maps it with you.
- Map your SSIDs onto threeOpen, secure and xPSK, on the access points you already own. You leave with the plan.
- Prove it on one site firstJudge the result on tickets and audit evidence, then roll out.
Your design session
45 minutes. Your estate. A plan you keep.
Led by a Purple network engineer. No slides. You keep the plan.